Meaning
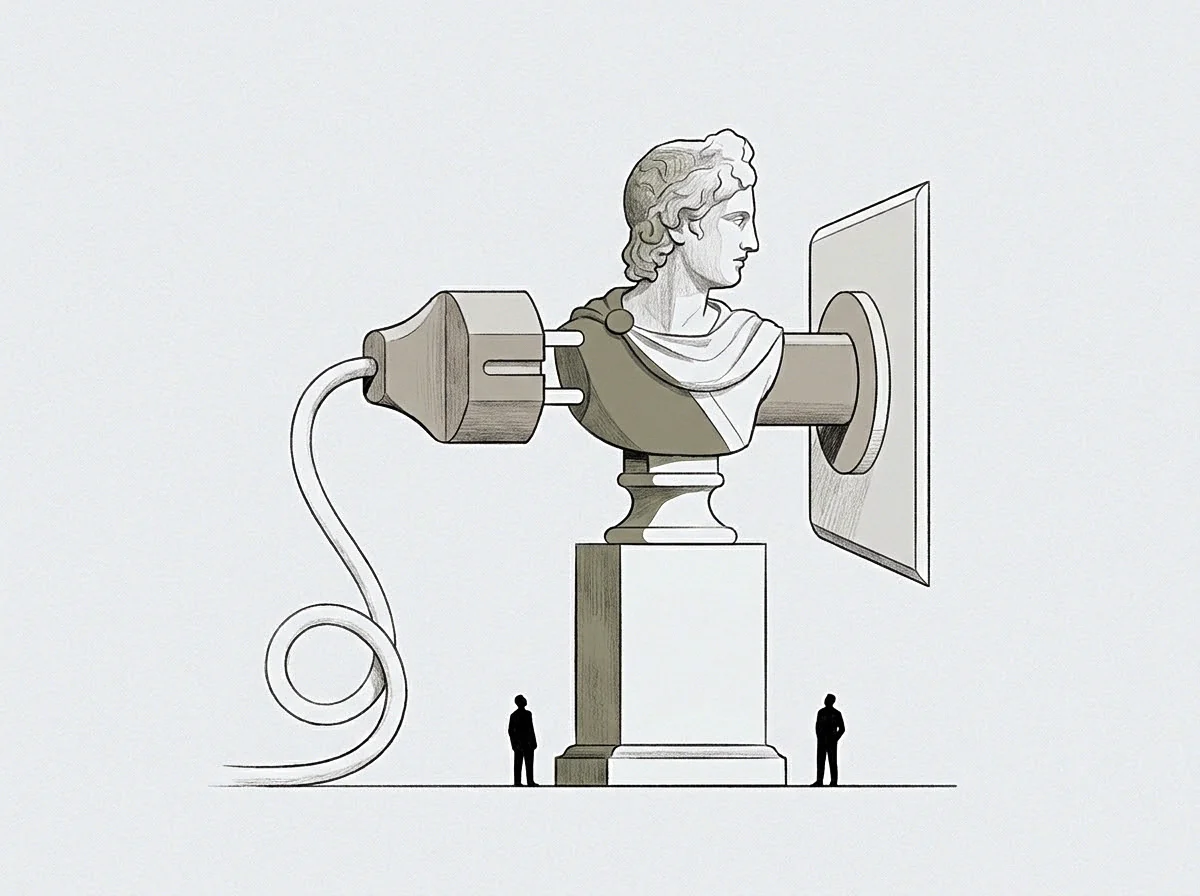
A procedural mechanism allows an administrator to bypass predefined software restrictions to execute commands outside normal operating parameters. A system override provides access to root-level functions that remain otherwise locked during routine production cycles. This capability functions by suspending internal logic checks or security protocols that prevent unauthorized inputs.
It defines the boundary where automated governance ends and manual intervention begins.
Control Limit
An intentional breach of programmed constraints carries distinct administrative risks concerning data integrity and configuration stability. When a system override executes, the audit trail captures the identity of the actor and the precise timestamp of the modification. This record stands as primary evidence in later disputes over unauthorized changes to core infrastructure.
The logs prove the sequence of actions taken while the safety interlocks remained inactive.
Operation Protocol
Personnel apply these manual permissions only when a catastrophic failure or deadlock prevents standard software functionality. Applying the sequence requires a formal authorization request that persists as a permanent part of the technical documentation. The process necessitates a secondary verification step to ensure the scope of the change remains limited to the reported fault.
If the modification occurs without such documentation, the record loses its status as a verifiable proof of administrative necessity.
Performance Impact
Every instance of manual intervention consumes significant oversight hours to verify the post-action state of the architecture. A system override creates a divergence from the expected software configuration that lasts until the next code deployment or manual reconciliation. This deviation often increases the complexity of future maintenance because the environment no longer matches the documented baseline.
Continuous reliance on these forced states suggests a structural deficiency in the automated governance model.